Technical Craft
Map a Mobile Game’s Data Before Writing Its Privacy Page
Inventory collection, purpose, processors, retention, deletion, and store disclosures before making public claims.
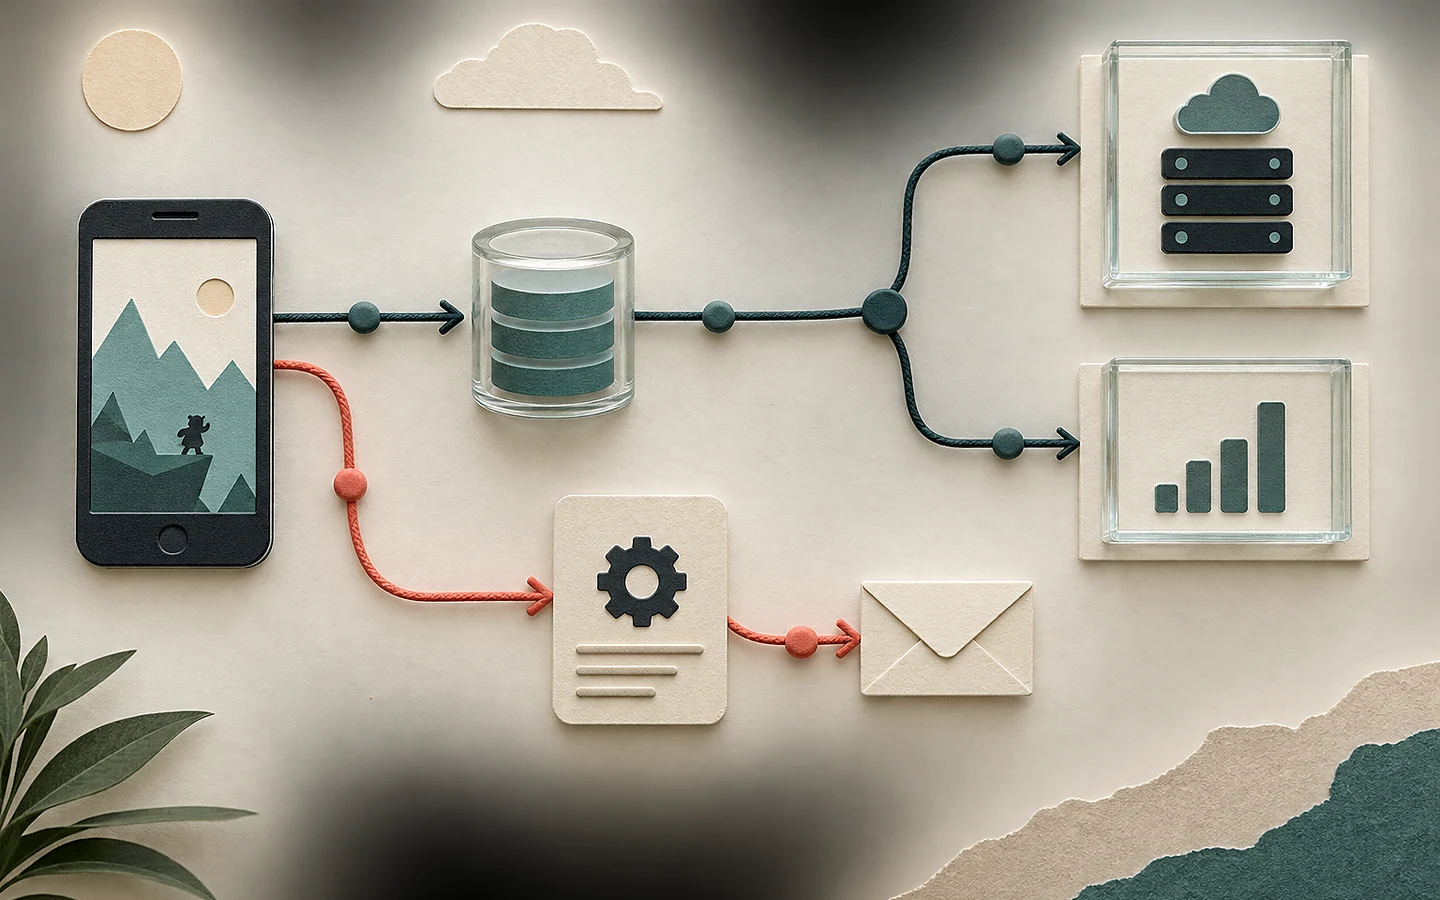
A privacy page should describe the product that exists, not the product a template imagined. Before writing legal-style prose, map every path by which a game, website, SDK, support process, and hosting provider receives or stores data. Store disclosures and public policy text should be derived from the same inventory.
Start with events, not vendor names
List actions that can create data: install, launch, account creation, authentication, purchase, ad request, crash, multiplayer session, chat, support message, newsletter signup, website visit, and deletion request. For each event, record fields, purpose, destination, storage, retention approach, user choice, and whether it is linked to an account or device.
Then map vendors and SDKs to those events. An analytics package may collect more than the calls visible in gameplay code. Review its configuration, platform manifest, dashboard settings, and current documentation. Recheck after SDK updates because defaults and data paths can change.
Distinguish collection, sharing, and local processing
Platform definitions matter. Data kept only on the device may be treated differently from data sent to a developer-controlled server. A processor acting on the developer’s behalf may be disclosed differently from an advertising partner using data for its own purposes. Follow the current store questionnaire and seek qualified advice for legal conclusions.
Do not assume that hashing makes an identifier anonymous. If a value can still relate activity to a device or account, describe that relationship accurately. Minimize collection before searching for more elaborate policy language.
A worked example: crash reporting plus ads
Consider a free mobile game with crash reporting and an ad SDK. The map lists crash stack, app version, device model, operating-system version, session identifier, advertising identifier, IP-derived region, ad impressions, and purchase status. It separates fields sent for diagnostics from those used for ad delivery or measurement.
The team discovers that personalized advertising is enabled by default in one region and that the crash service retains identifiers longer than expected. The correct response is operational: change configuration, document consent behaviour, shorten retention where supported, and retest requests. Rewording the privacy page alone would not fix the mismatch.
Connect user requests to real operations
A deletion statement needs a route, identity-verification method proportionate to the account, systems to search, processor requests, exceptions, and a completion record. If the game has no account, explain what can and cannot be associated with a requester. Never ask users to email passwords, payment details, or unnecessary identity documents.
Use one monitored contact address consistently across the site, store listing, and in-app support. Give users the information they need to identify the product and request type. Do not promise a response time or jurisdiction-specific right unless the operator can honour and verify it.
Maintain one evidence record
Keep the data map, SDK versions, configuration screenshots, request samples, policy revision, store answers, and review date together. Assign responsibility to an organization or named person who can correct the record. Marketing copy, consent screens, and support scripts should not contradict it.
Our editorial judgment is that a shorter accurate inventory is safer and more useful than a sweeping template. This guide is a production checklist, not legal advice. Products serving children, processing sensitive data, or operating across jurisdictions need qualified review based on their actual audience and data flow.
Sources and verification
Primary documentation checked on 25 September 2026. Product and platform requirements can change; recheck the linked source before release work.